2024“龙信杯“电子数据取证竞赛——计算机取证题目Writeup
以下内容是2024年“龙信杯”电子数据取证竞赛计算机取证题目的答案与解题思路
前置
前置发现电脑中有EFS加密文件,故使用仿真软件保持原有密码进行仿真
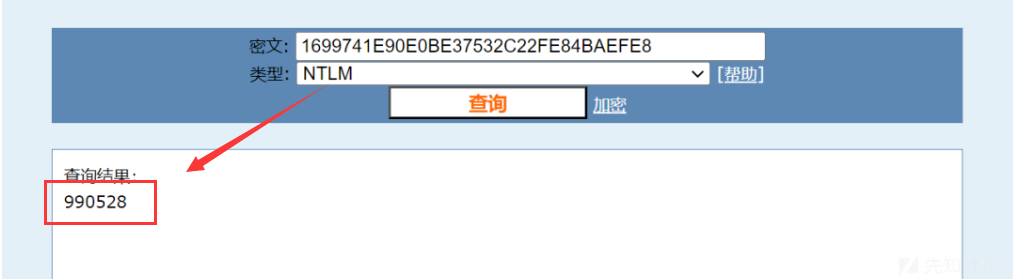
1.分析计算机检材,嫌疑人在将其侵公数据出售前在Pycharm中进行了AES加密,用于加密的key是多少?[标准格式:1A23456ABCD]
参考答案:65B2564BG89F16G9
解题思路:使用仿真软件对计算机检材进行仿真,打开桌面Pycharm软件,发现encrypted.py脚本,定位key值。
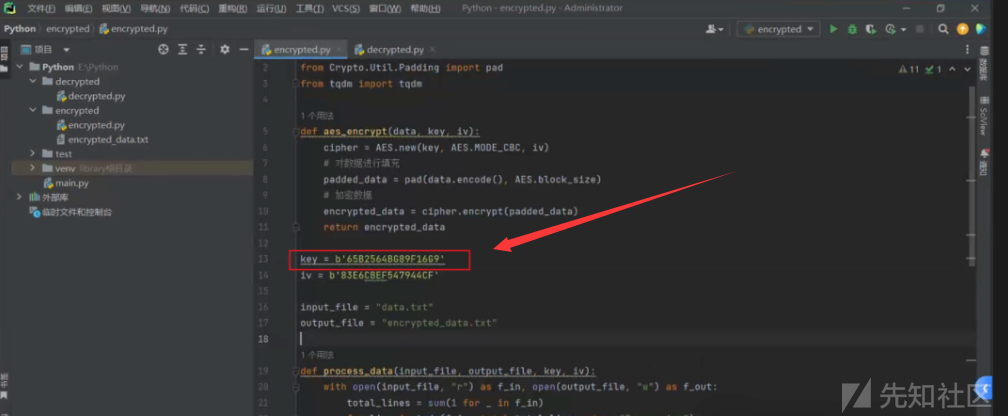
2.分析计算机检材,身份证为"371963195112051505"这个人的手机号码是多少?[标准格式:13013524420]
参考答案:15075547510
解题思路:
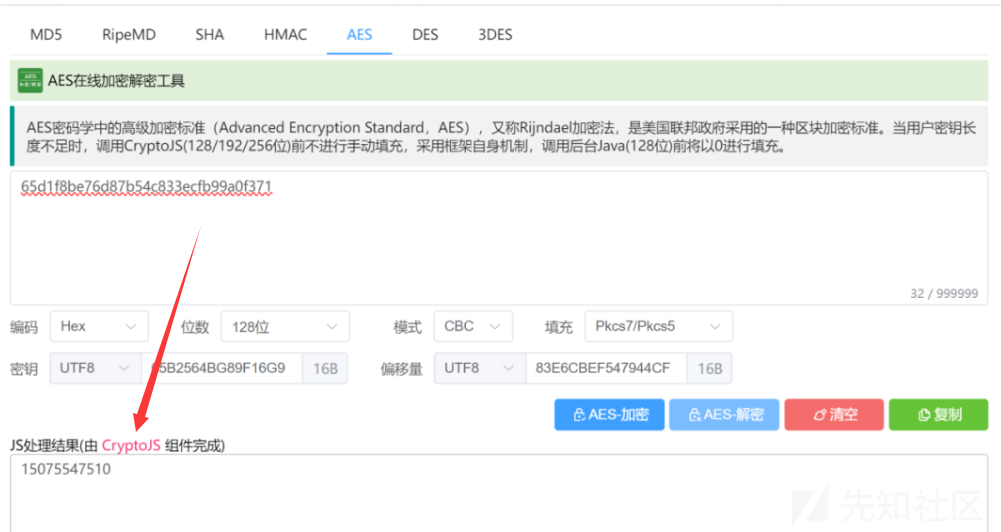
2.1根据key"65B2564BG89F16G9"、iv"83E6CBEF547944CF"对身份证"371963195112051505"进行加密
在线加密地址:https://www.mklab.cn/utils/aes
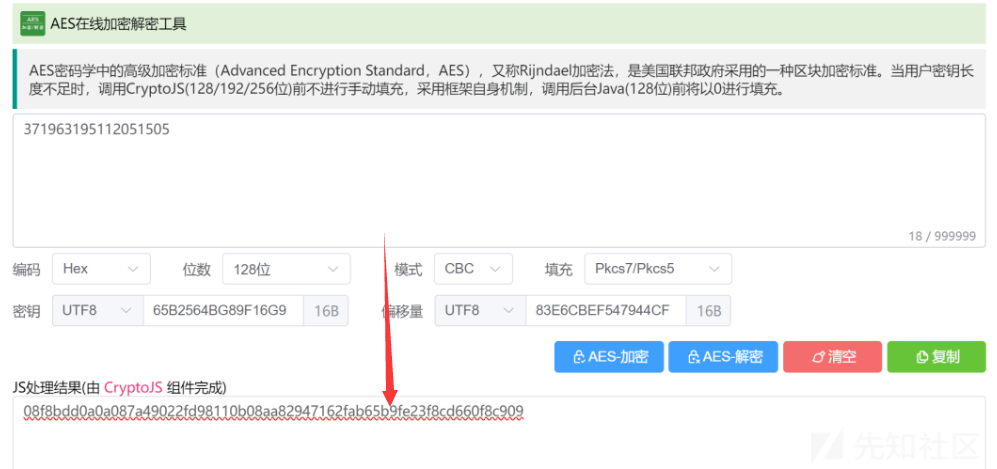
2.2 在文件中搜索对应值,解密当行其他值
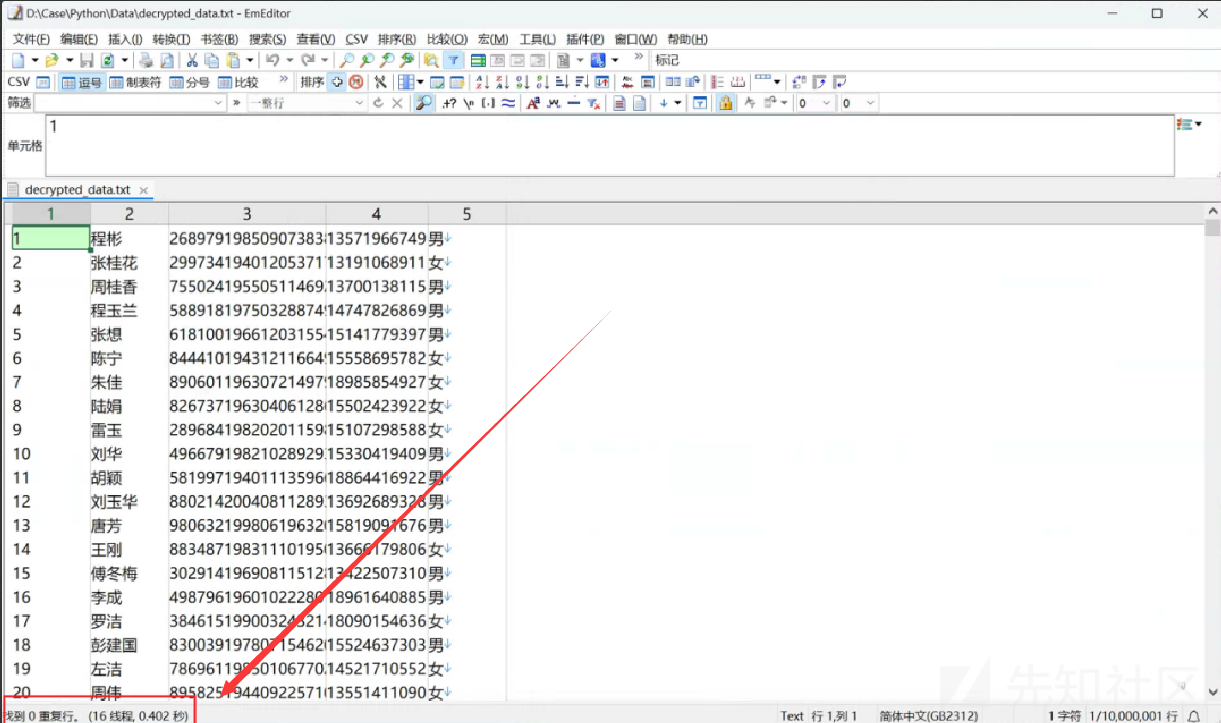
3.分析计算机检材,对解密后的身份证数据列进行单列去重操作,重复的身份证号码数量是多少?(身份证不甄别真假)[标准格式:100]
参考答案:0
解题思路:
3.1 对加密文件“encrypted_data.txt”进行解密,编写代码如下:
import os
import
time
from Crypto.Cipher import AES
from
Crypto.Util.Padding import unpad
from concurrent.futures import
ProcessPoolExecutor, as_completed
from tqdm import tqdm

defaes_decrypt(encrypted_data, key, iv):

    cipher =AES.new(key, AES.MODE_CBC, iv)

    decrypted_data =cipher.decrypt(encrypted_data)

    unpadded_data =unpad(decrypted_data, AES.block_size)

    returnunpadded_data.decode("utf-8")

defprocess_chunk(lines, key, iv):

    result =[]

    for line inlines:

        parts =line.strip().split(',')

       index = parts[0]


       decrypted_parts = [index]


      for part inparts[1:]:

           encrypted_part = bytes.fromhex(part)


           decrypted_part =aes_decrypt(encrypted_part, key, iv)

           decrypted_parts.append(decrypted_part)

       result.append(",".join(decrypted_parts)+ "\n")


   return result

defget_file_line_count(file_path):

    withopen(file_path, 'r', encoding='utf-8')
as f:

        line_count = sum(1for _ inf)

    return line_count

defprocess_data(input_file, output_file, key, iv, num_workers=32,
chunk_size=10000):


   total_lines =get_file_line_count(input_file)

    num_workers =min(num_workers, os.cpu_count() * 2)


   withProcessPoolExecutor(max_workers=num_workers)
as executor, \

            open(input_file, "r")
as f_in, \

            open(output_file, "w")
as f_out:

        futures = []


       lines_processed = 0


       pbar = tqdm(desc="解密进度",
unit="行",
total=total_lines)


       try:

            whileTrue:

                lines =[f_in.readline() for _ inrange(chunk_size)]

                lines =list(filter(None, lines))


      if notlines:

                    break

                future =executor.submit(process_chunk, lines, key, iv)

               futures.append((future, len(lines)))

                forfuture, num_lines in futures:


                   iffuture.done():

                        result =future.result()

                       f_out.writelines(result)

                       lines_processed += num_lines


                  pbar.update(num_lines)


 futures.remove((future, num_lines))

        exceptKeyboardInterrupt:

           print("\n用户中断操作。")


       except Exceptionas e:

            print(f"处理数据时发生错误:{e}")


       finally:

           for future, num_lines infutures:

                try:


                   result =future.result()

                    f_out.writelines(result)


                   lines_processed +=num_lines

                    pbar.update(num_lines)


           except Exceptionas e:

                    print(f"处理剩余任务时发生错误:{e}")


   pbar.close()

    print(f"解密完成。共解密{lines_processed}行数据。")

if__name__ =='__main__':

    key =b'65B2564BG89F16G9'

    iv =b'83E6CBEF547944CF'

    input_file= "../encrypted_data.txt"


   output_file = "decrypted_data.txt"


   start_time = time.time()

   print("开始解密...")


   try:

       process_data(input_file, output_file, key, iv, num_workers=64)


   except Exceptionas e:

        print(f"处理数据时发生错误:{e}")


   end_time = time.time()

   print(f"总耗时:{end_time -start_time} 秒")
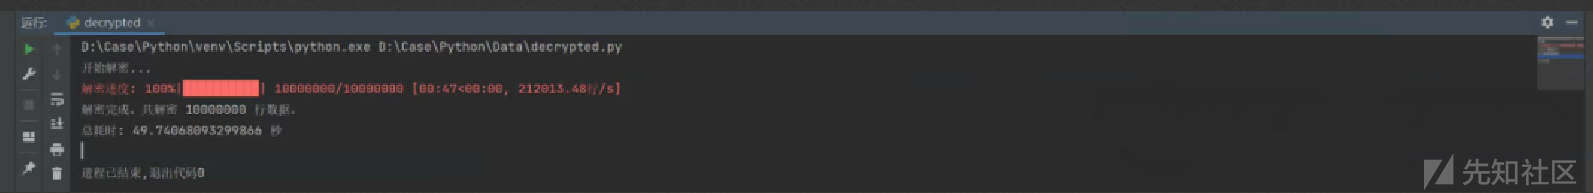
3.2 使用EmEditor对身份证列进行去重操作
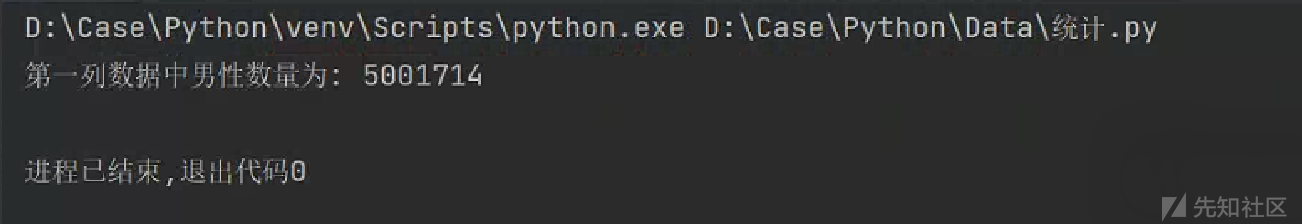
4.分析计算机检材,接上题,根据身份证号码(第17位)分析性别,男性的数据是多少条?[标准格式:100]
参考答案:5001714
解题思路:
4.1根据身份证的特性(第17位)来判断男性还是女性,其中奇数分配给男性,偶数分配给女性,编写代码如下:
import threading
from tqdm import tqdm
import os

defread_file_with_encoding(file_path, encoding):

    try:


       with open(file_path, 'r',
encoding=encoding) as file:


    return file.readlines()


   except UnicodeDecodeError:


       return None

defprocess_line(line):

    try:


       _, _, id_number, _, original_gender =line.strip().split(',')

    exceptValueError:

        print(f"数据格式错误:{line.strip()}")


       return None

    iflen(id_number) == 18:


       gender_digit = id_number[16] # 第17位(0-based index)

        ifgender_digit.isdigit():

            analyzed_gender ='男' ifint(gender_digit) % 2!= 0 else'女'


      else:

           print(f"身份证号码格式错误:{id_number}")


           return None

   else:

       print(f"身份证号码长度错误:{id_number}")


       return None

   returnf"{analyzed_gender},{original_gender}\n"

defworker(lines, results, lock, pbar):

    local_results =[]

    for line inlines:

        result =process_line(line)

        ifresult:

            local_results.append(result)

       pbar.update(1)

    withlock:

        results.extend(local_results)

defmain():

    file_path ='decrypted_data.txt'

    ifnot os.path.exists(file_path):


       print(f"文件{file_path}不存在,请检查文件路径。")


       return

    lines =read_file_with_encoding(file_path, 'utf-8')


   if lines isNone:

        lines =read_file_with_encoding(file_path, 'gbk')


       if lines isNone:

            return

   total_entries = len(lines)

   num_threads = 8


   chunk_size = total_entries //num_threads

    threads = []


   results = []

    lock =threading.Lock()

    pbar =tqdm(total=total_entries, desc="处理进度",
unit="条")


   for i inrange(num_threads):

        start =i * chunk_size

        end =None ifi == num_threads -1 else(i + 1) *chunk_size

        thread =threading.Thread(target=worker,
args=(lines[start:end], results, lock,
pbar))

        threads.append(thread)

       thread.start()

    forthread in threads:

       thread.join()

    pbar.close()

    withopen('result.txt', 'w',
encoding='utf-8')
as outfile:

        forline in results:


 outfile.write(line)

    print("数据分析和写入result.txt 完成。")

if__name__ =='__main__':

    main()
4.2 分析上述生成的result.txt文件,编写代码如下:
import os

defcount_males_in_result(file_path):

    male_count =0

    withopen(file_path, 'r', encoding='utf-8')
as infile:

        for linein infile:

           analyzed_gender, _ =line.strip().split(',')

           if analyzed_gender =='男':


               male_count += 1


   return male_count

defmain():

    result_file_path ='result.txt'

    ifnotos.path.exists(result_file_path):

        print(f"文件{result_file_path}不存在,请先生成结果文件。")


       return

    male_count =count_males_in_result(result_file_path)

   print(f"第一列数据中男性数量为:{male_count}")

if__name__ =='__main__':

    main()
5.分析计算机检材,接上题,对解密后的数据文件进行分析,甄别身份证号码性别值与标识性别不一致的数量是多少?[标准格式:100]
参考答案:5001185
解题思路:
分析上述生成的result.txt文件,编写代码如下:
import os
from
tqdm import tqdm

defcount_mismatched_entries(file_path):

    mismatch_count =0

    total_entries =0

    withopen(file_path, 'r', encoding='utf-8')
as infile:

        for linein tqdm(infile, desc="Counting
mismatched entries"):

            analyzed_gender,
original_gender =line.strip().split(',')

           total_entries += 1


           if analyzed_gender !=original_gender:

                mismatch_count +=1

    returnmismatch_count, total_entries

defmain():

    result_file_path ='result.txt'

    ifnotos.path.exists(result_file_path):

        print(f"文件{result_file_path}不存在,请先生成结果文件。")


       return

    mismatch_count, total_entries =count_mismatched_entries(result_file_path)

   print(f"不一致的数据量为:{mismatch_count},总数据量为:{total_entries}")

if__name__ =='__main__':

    main()

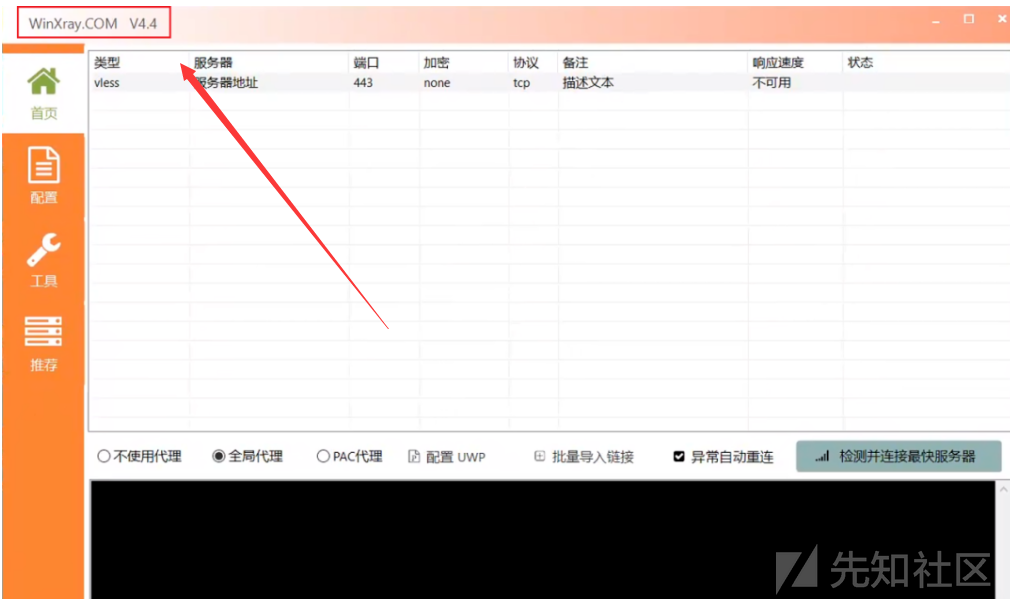
6.分析计算机检材,计算机中存在的“VPN”工具版本是多少?[标准格式:1.1]
参考答案:4.4
解题思路:在E:\WinXray\WinXray.exe发现VPN软件
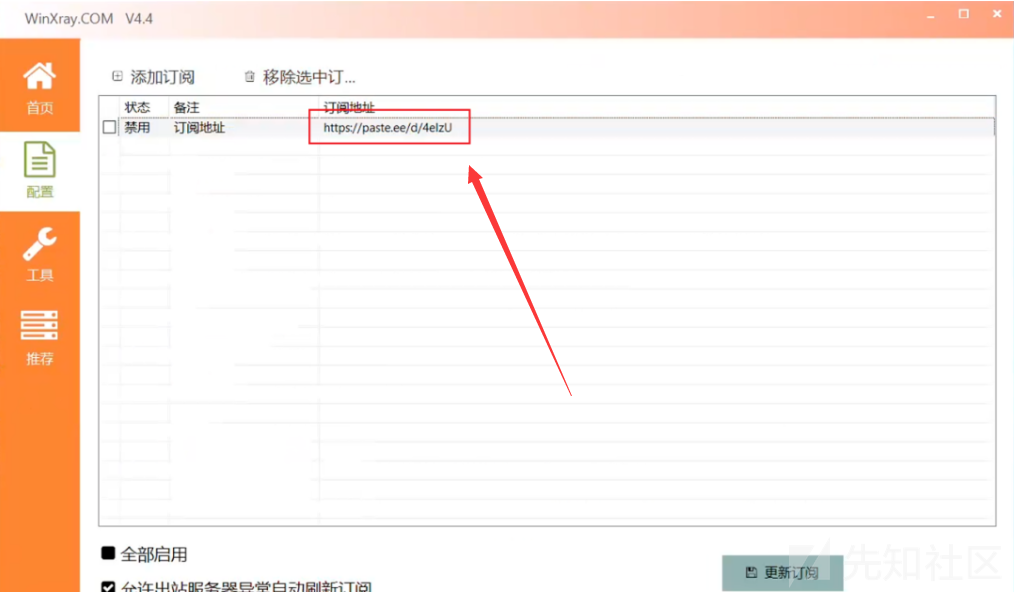
7.分析计算机检材,计算机中存在的“VPN”节点订阅地址是什么?[标准格式:http://xxx.xx/x/xxx]
参考答案:https://paste.ee/d/4eIzU
解题思路:
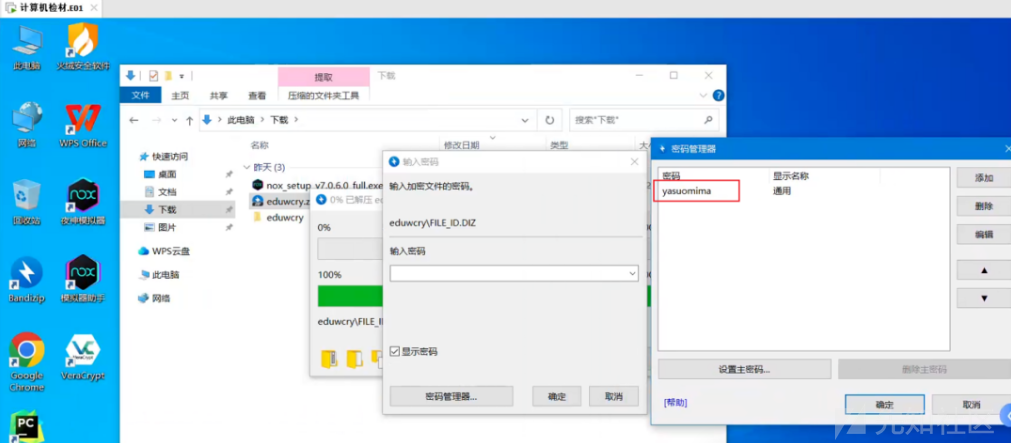
8.分析计算机检材,eduwcry压缩包文件的解压密码是什么?[标准格式:abcabc]
参考答案:yasuomima
解题思路:
在"C:\Users\Administrator\Downloads"路径下发现eduwcry压缩包,在bandzip发现通用密码,尝试解压成功。
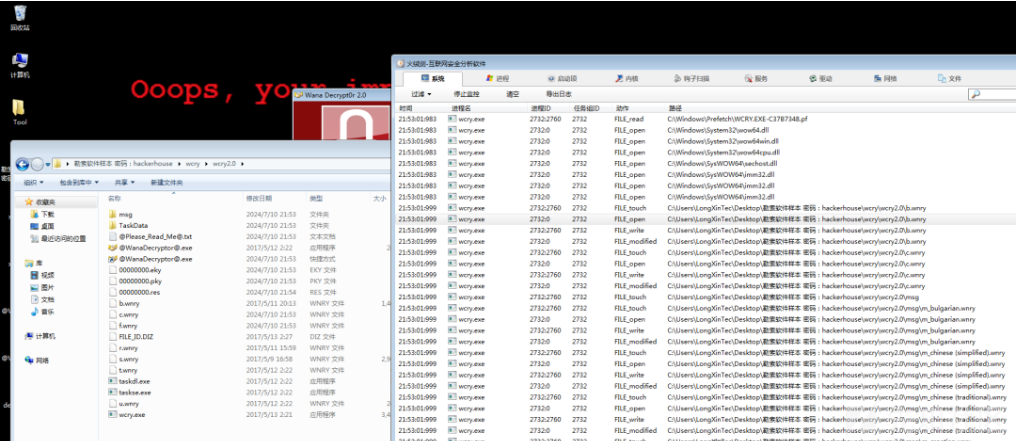
9.分析计算机检材,接上题,请问恶意程序释放压缩包的md5值是多少。[标准格式:全小写]
参考答案:b576ada3366908875e5ce4cb3da6153a
解题思路:
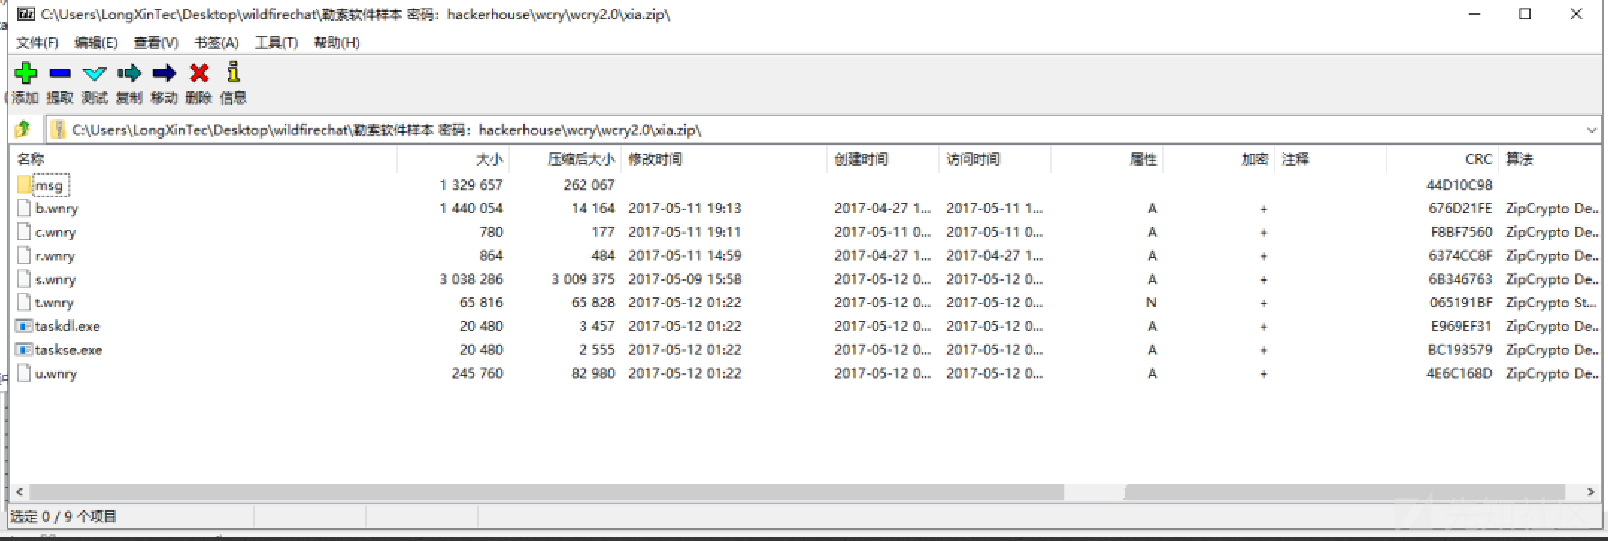
开启win7虚拟机运行wry.exe,使用火绒监视器发现软件运行时会释放相关文件
于是用ida进行静态分析,搜索wnry字符串得
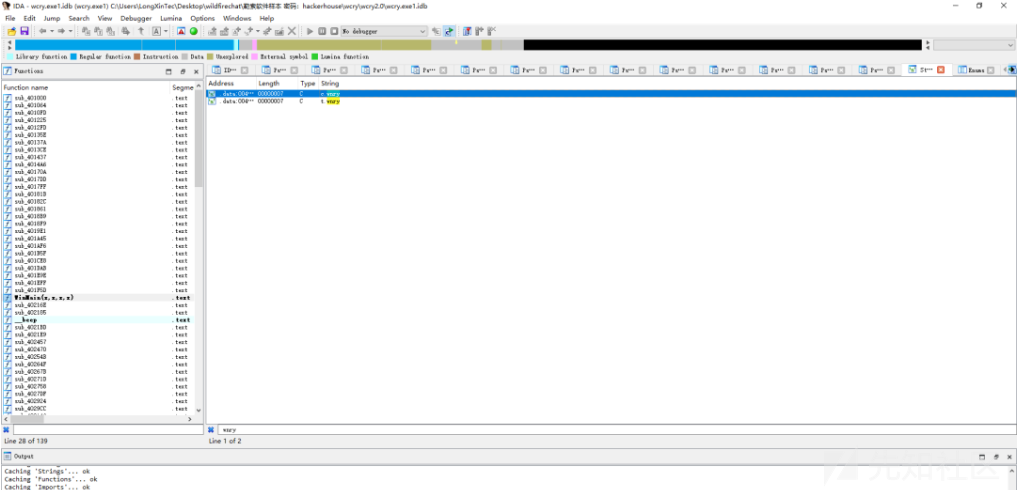
查看引用得sub_401DAB有个资源加载导出行为

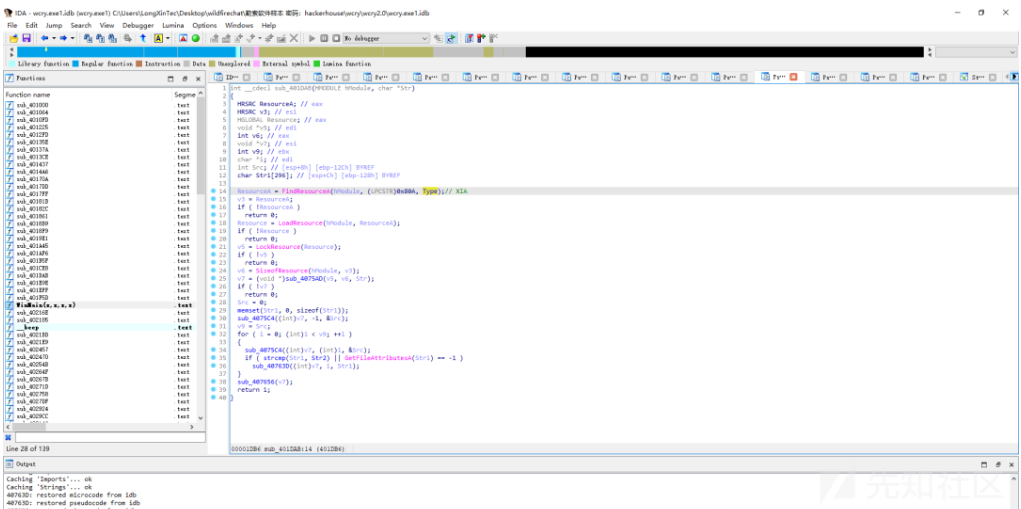
其中Type为XIA,于是使用工具cff进行分析exe,在资源结点找到XIA字符串
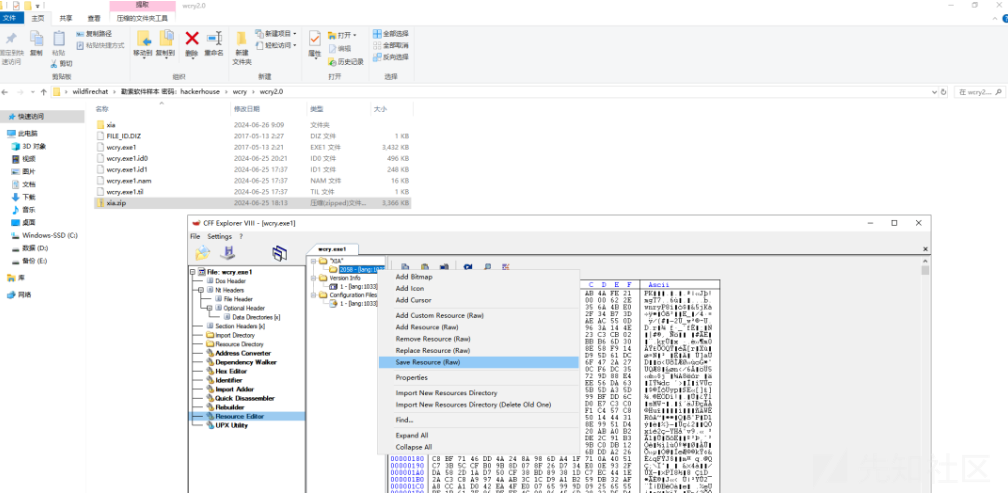
其子项2058内容为压缩包(PK签名)
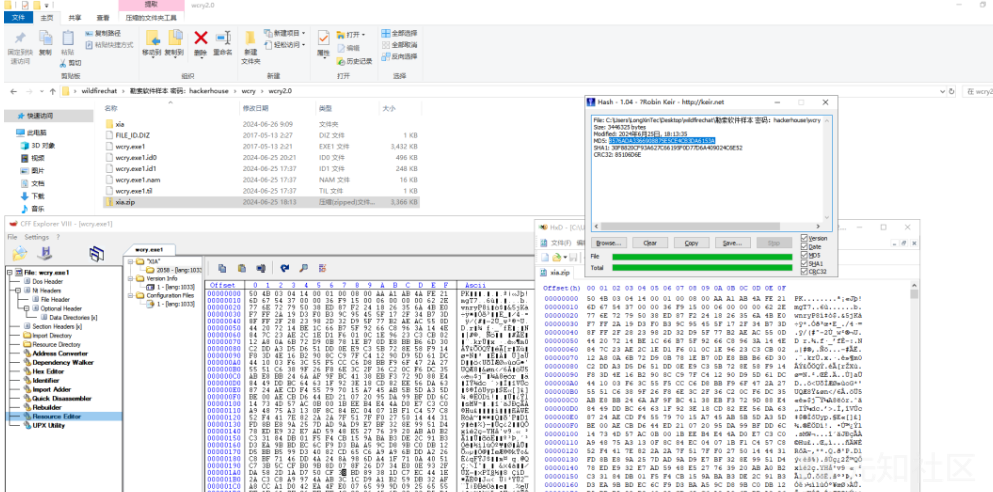
将其导出后用7z打开得与火绒监视得到的释放内容一致
10.分析计算机检材,接上题,请问恶意程序记录的洋葱浏览器下载地址是多少?[标准格式:http://xxx.xxx/xxx/xxx]
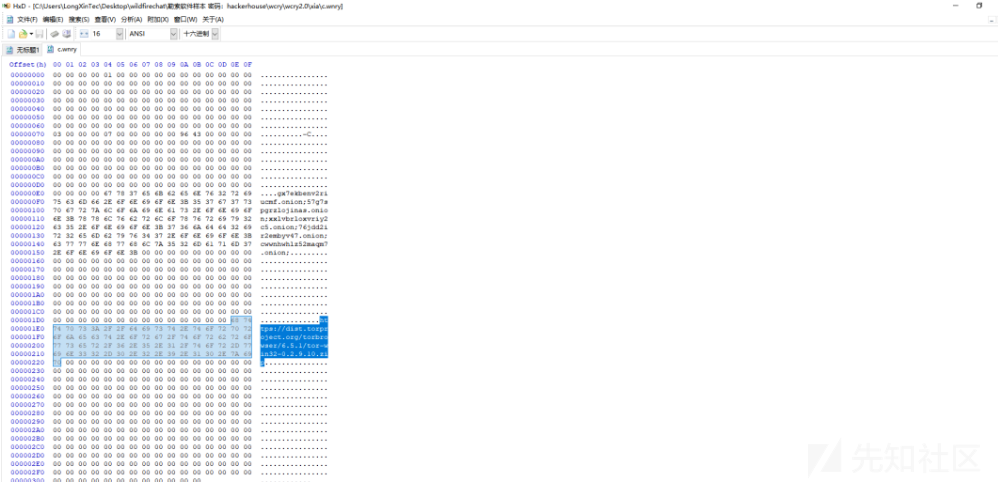
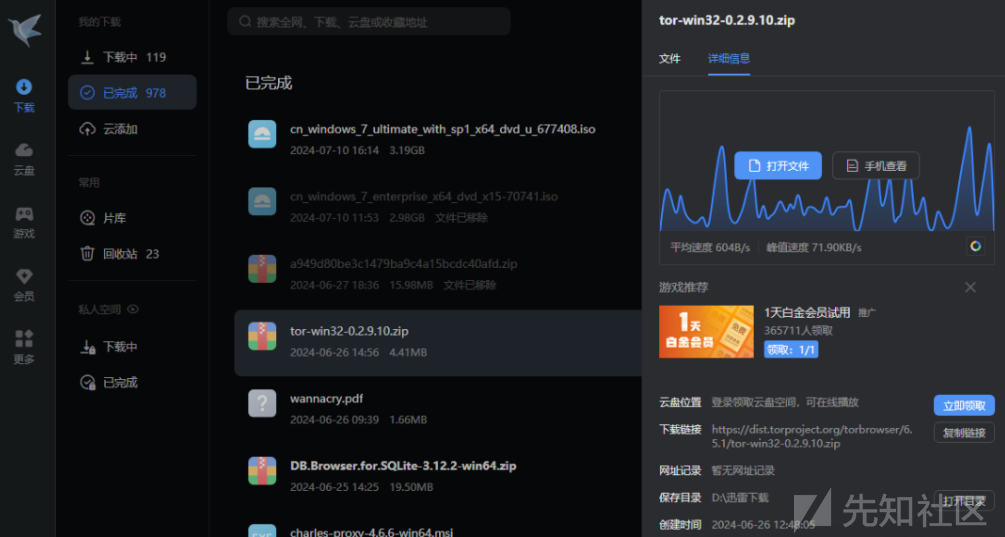
参考答案:https://dist.torproject.org/torbrowser/6.5.1/tor-win32-0.2.9.10.zip
解题思路:
软件在VM运行时,通过火绒剑监视发现@WannaDecryptor@.exe去打开s.wnry文件释放Tor.exe
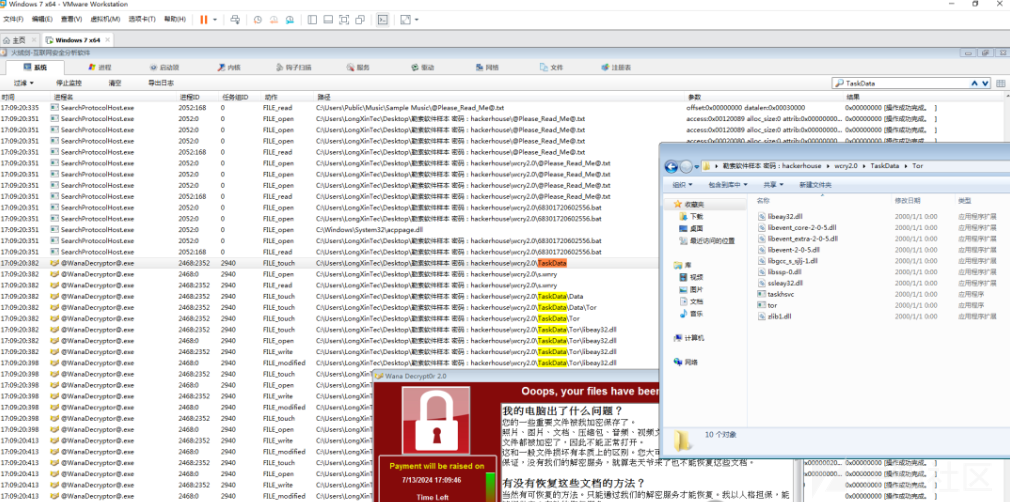
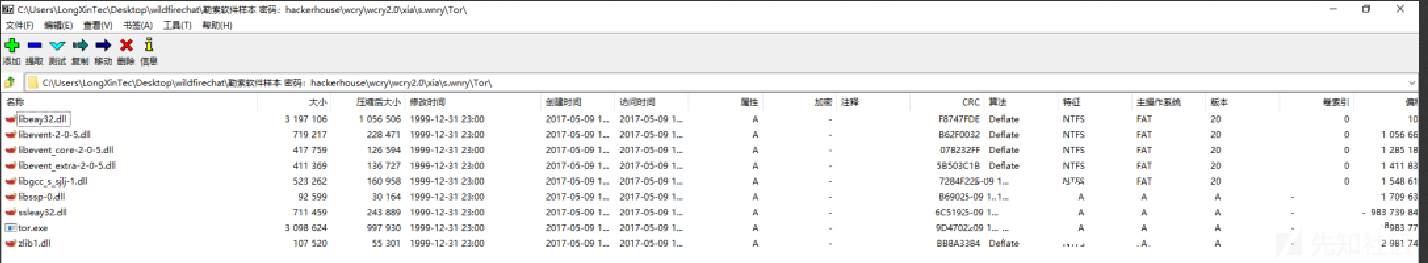
使用7z.exe打开s.wnry知该文件即为压缩包
于是全局搜索tor关键字发现c.wnry含有该链接
使用迅雷下载
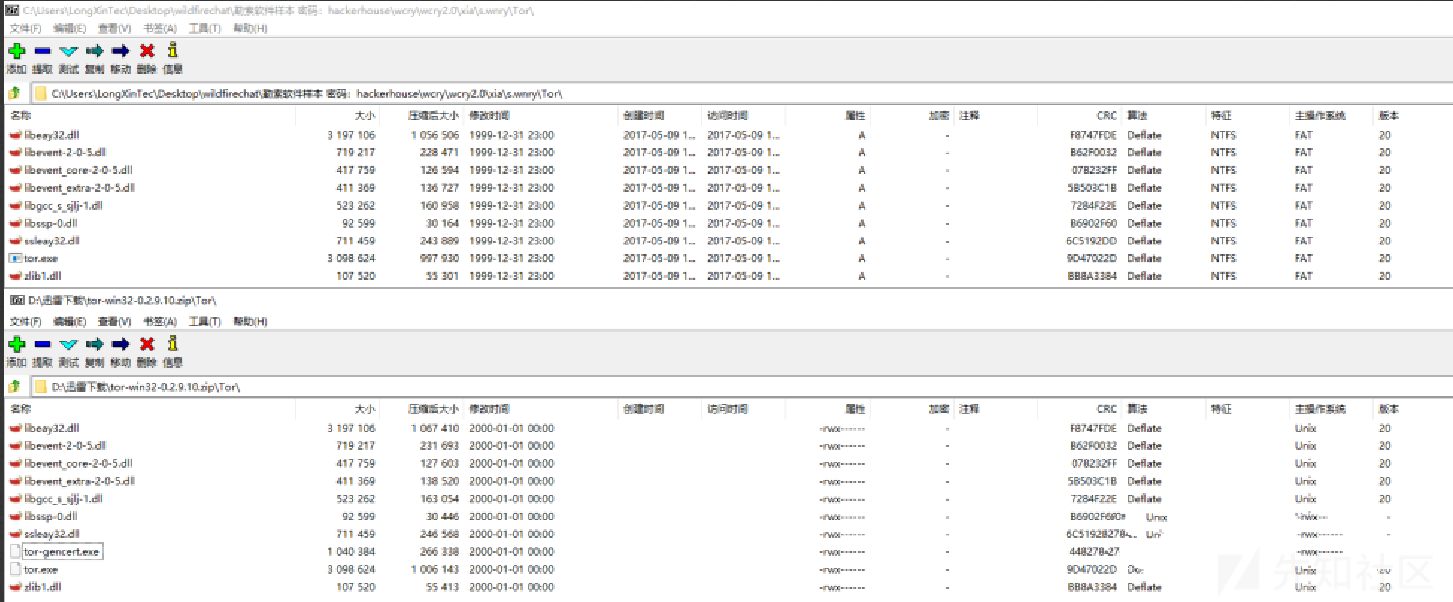
使用7z打开对比大小及crc值是一样的,故推断该浏览器是从这链接下载后精简的
11.分析计算机检材,接上题,请问恶意程序解密了t.wnry后该dll的md5值是多少。[标准格式:全大写]
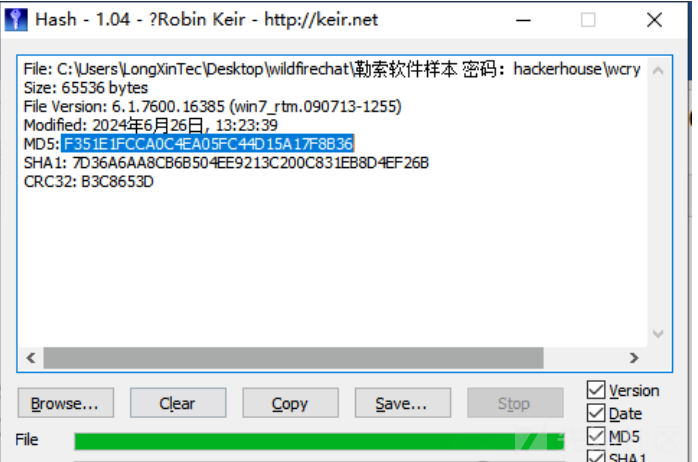
参考答案:f351e1fcca0c4ea05fc44d15a17f8b36
解题思路:
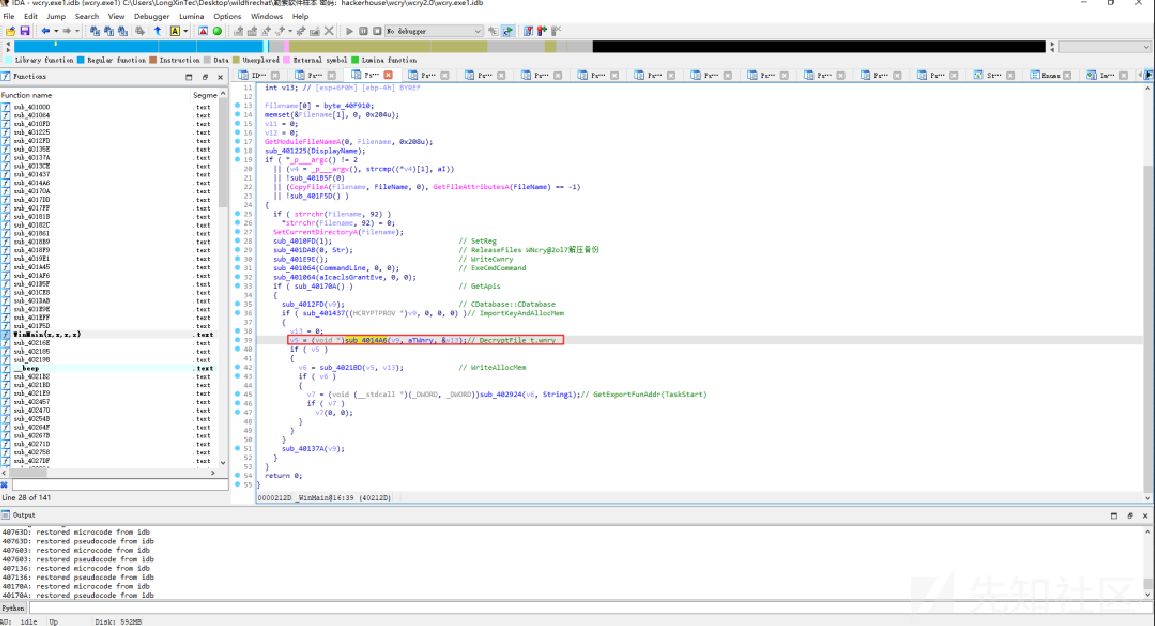
继续分析WinMain函数知sub_4014A6会对t.wnry进行解密,得到一个可执行程序(dll)然后通过sub_4021BD写入内存,最后通过sub_402924获取一个函数地址v7来调用
分析sub_4014A6函数
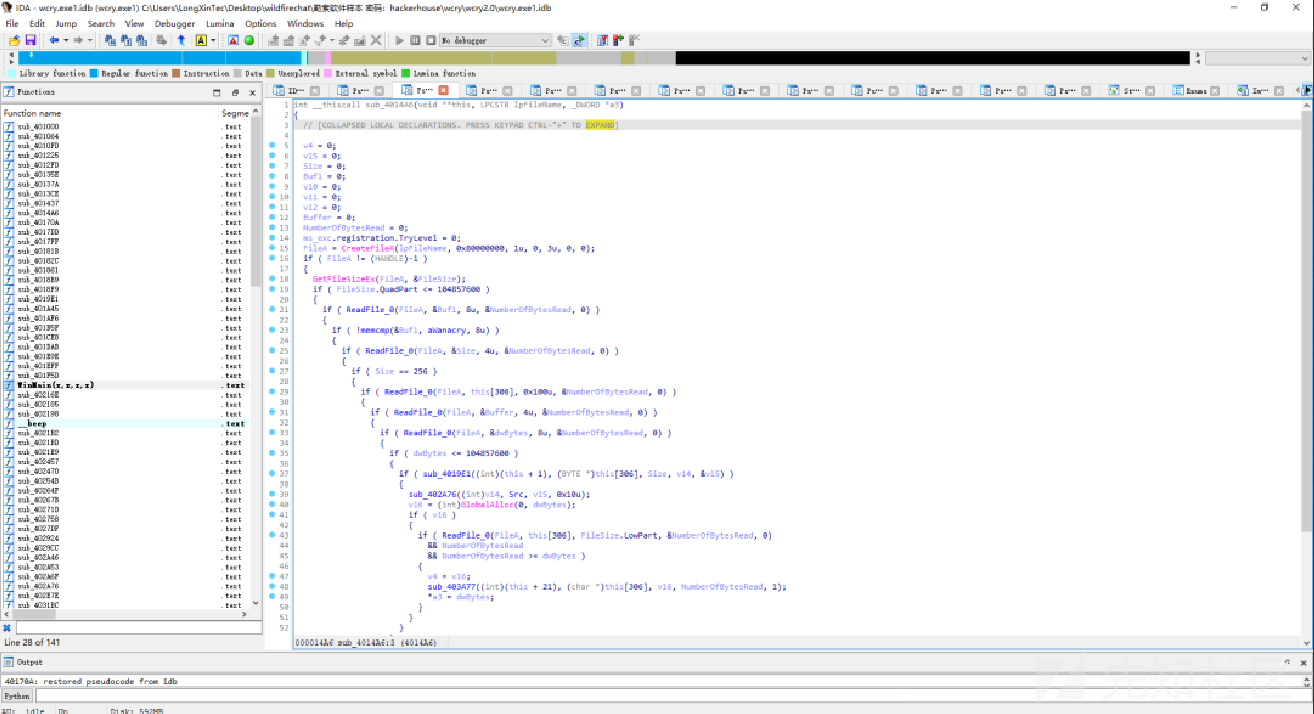
知v16在sub_403A77解密完成,于是使用xdbg进行动态调试,在sub_403A77处下断点
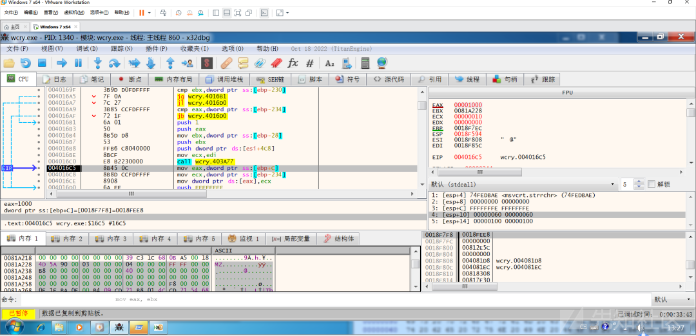
待执行完后对v16内容进行内存转储为t.dll文件,计算hash得
12.分析计算机检材,接上题,恶意程序运行起来后第一个循环调用了几次taskkill.exe。[标准格式:2]
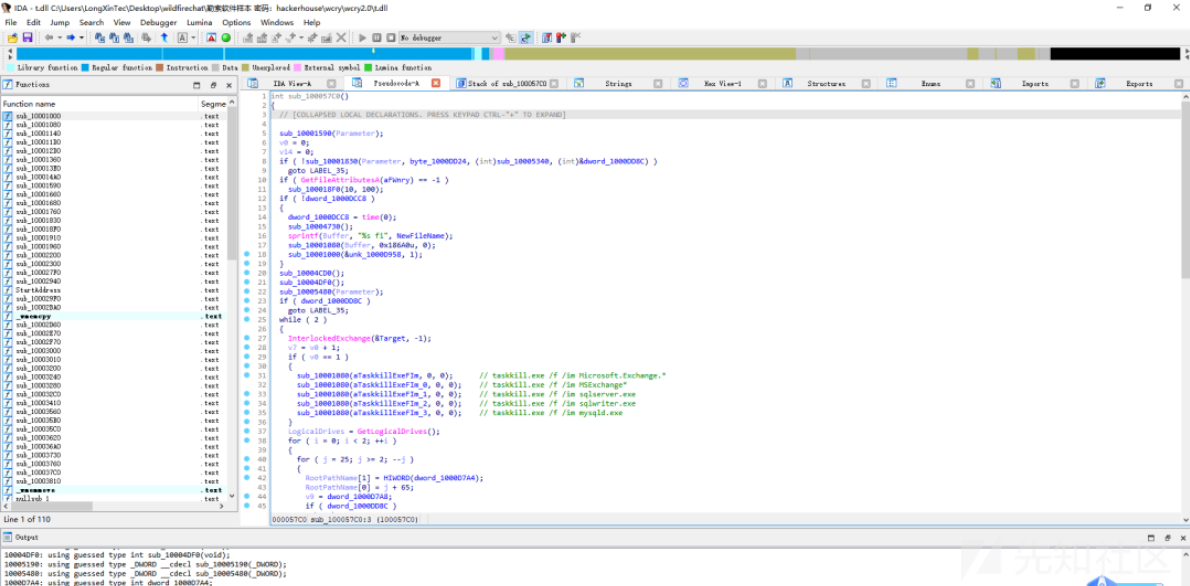
参考答案:5
解题思路:
使用ida分析t.dll,搜索taskkill引用情况
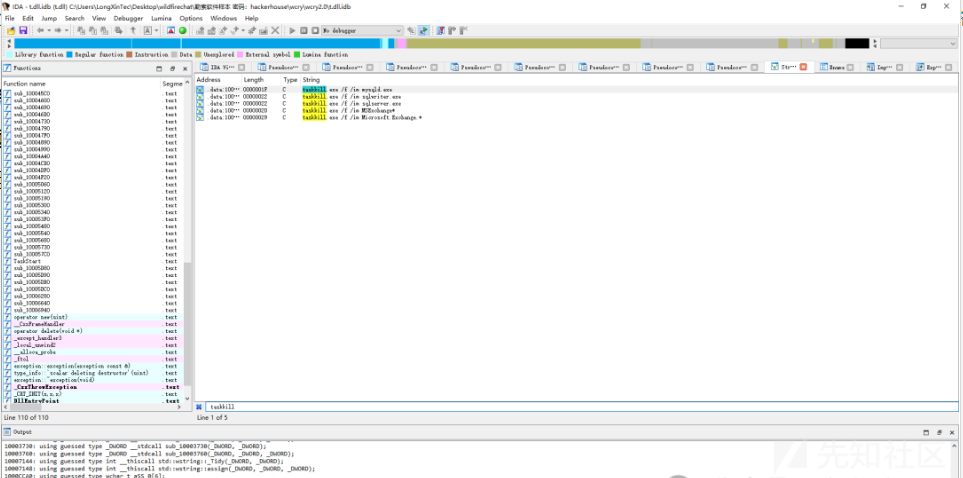
查看引用,知taskkill被sub_100057c0循环调用,v0==1调用了5次
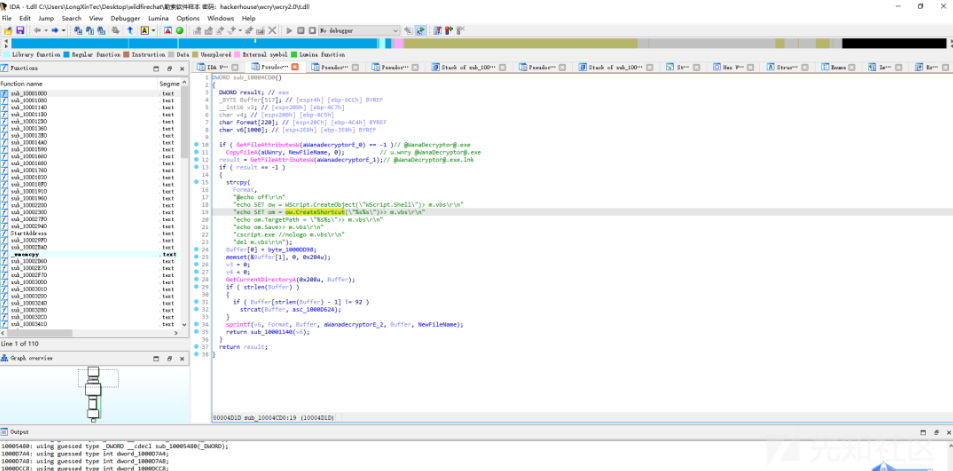
13.分析计算机检材,接上题,请问@WanaDecryptor@.exe.lnk文件是通过什么函数创建的。[标准格式:Aabcdef]
参考答案:CreateShortcut
解题思路:
搜索@WanaDecr yptor@.exe.lnk 字符串
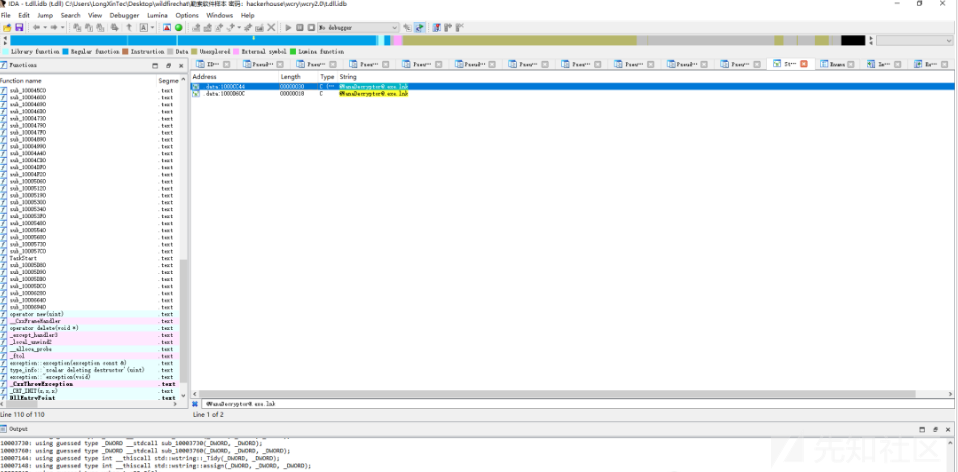
知该快捷方式在sub_10004CD0通过脚本创建(CreateShortcut)
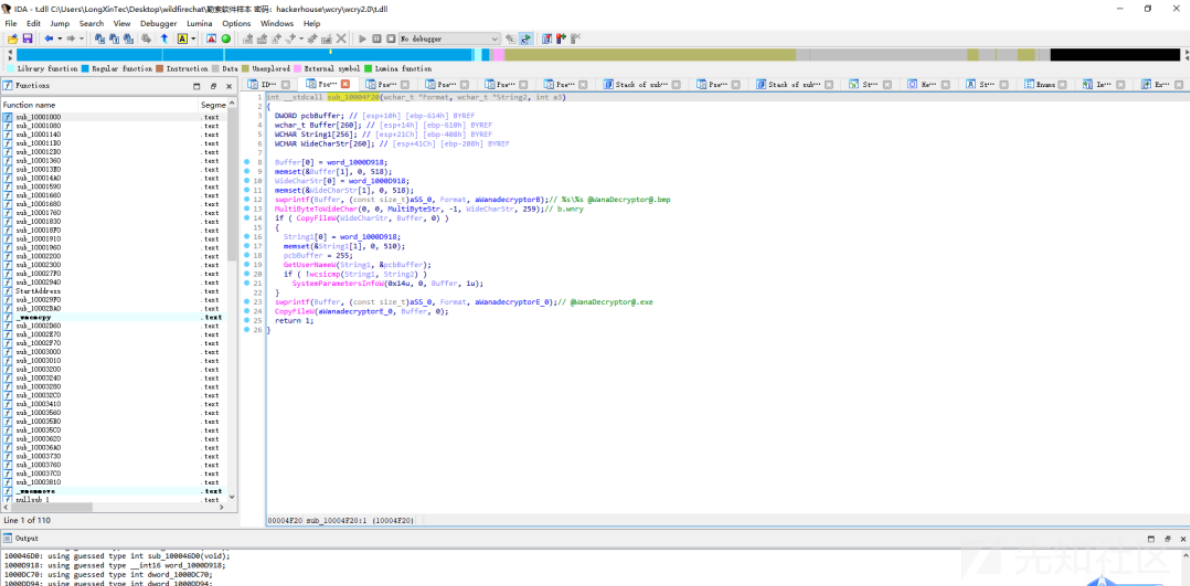
14.分析计算机检材,接上题,恶意程序修改系统桌面壁纸是在哪个函数实现的[标准格式:sub_xxx]
参考答案:sub_10004F20
解题思路:
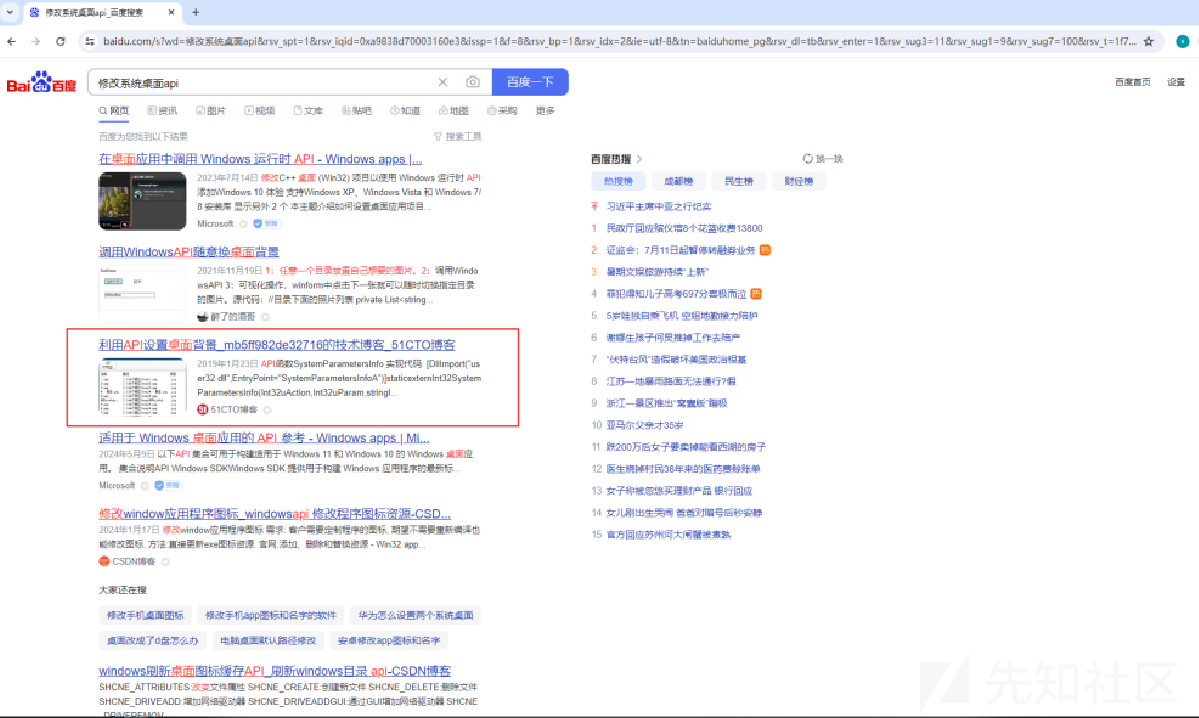
搜索修改系统桌面api得SystemParametersInfo
查看该api被sub_10004F20调用
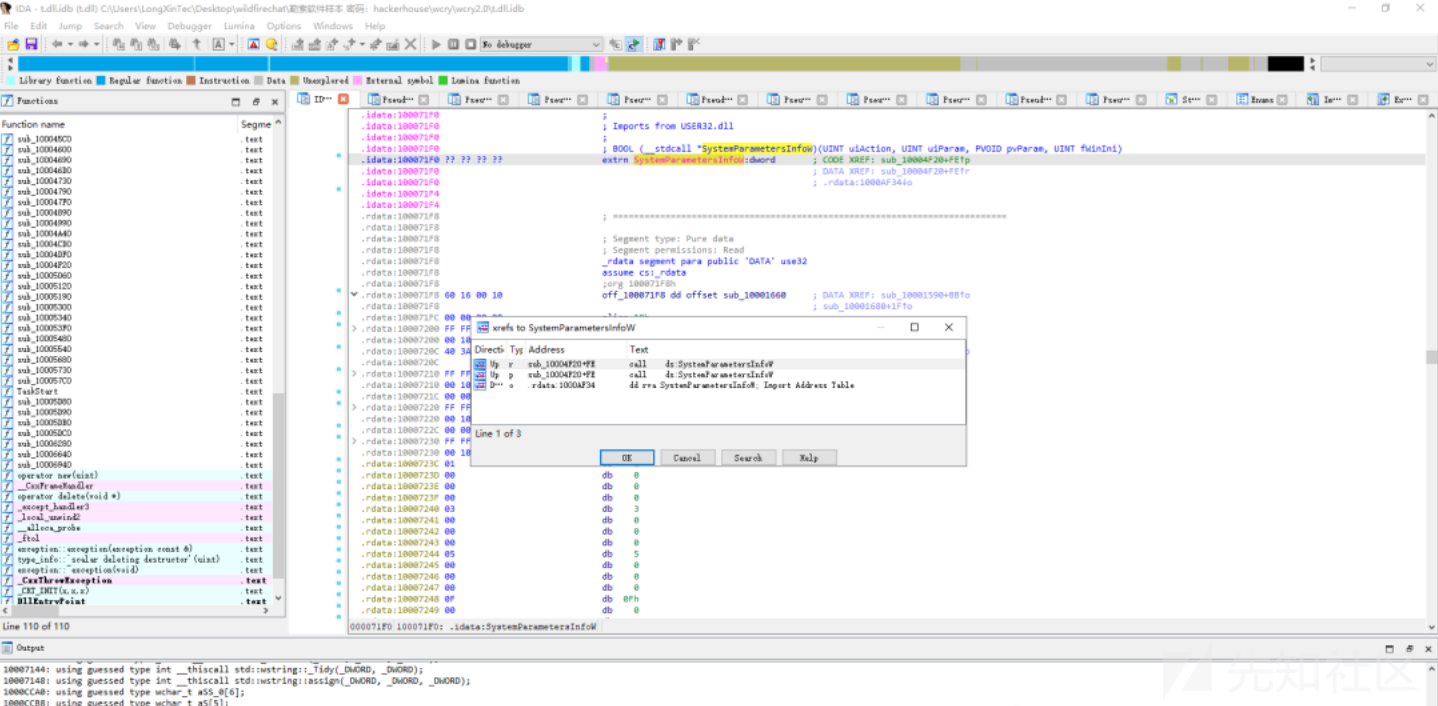
该函数将b.wnry文件内容写入到@WannaDecryptor@.bmp中,然后调用SystemParametersInfoW进行修改桌面
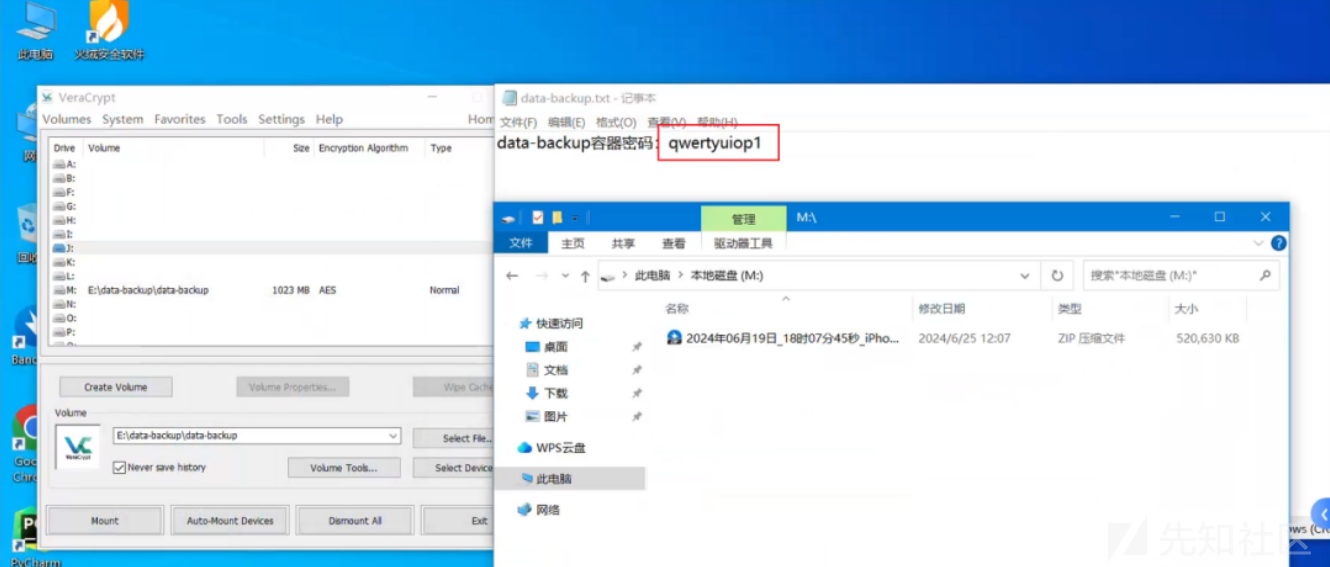
15.分析计算机检材,VeraCrypt加密容器的密码是什么?[标准格式:abc]
参考答案:qwertyuiop1
解题思路:
在E盘根目录找到疑似加密容器文件"data-backup.dd",经分析文件头是压缩包,将其解压。
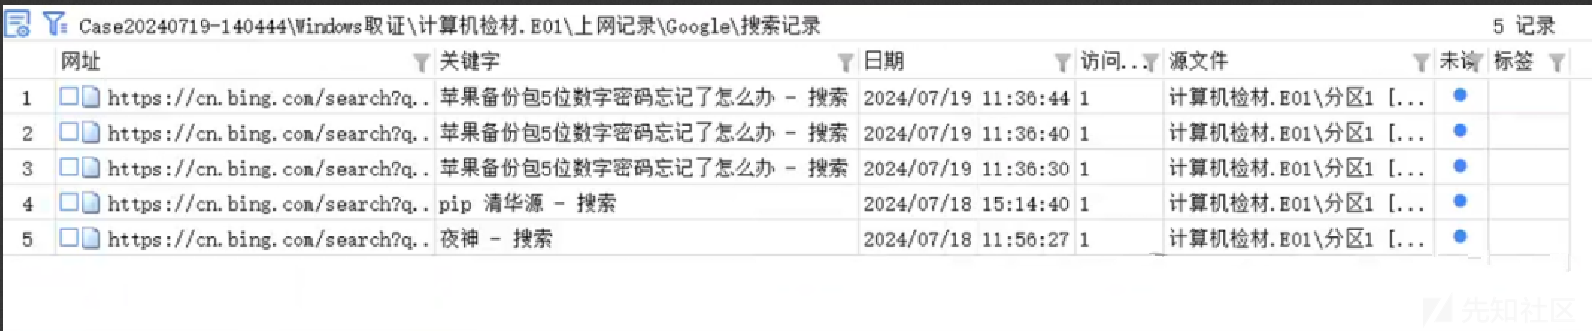
16.分析计算机检材,其中存在一个苹果手机备份包,手机备份包的密码是什么?[标准格式:12345]
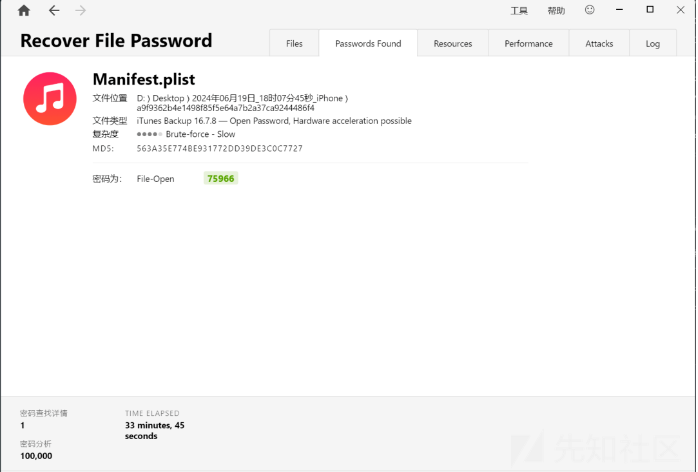
参考答案:75966
解题思路:通过Chrome浏览器搜索记录,确认苹果备份密码是5位
使用Passware Kit Forensic选择手机&云服务->iPhone Backup 自定义5位数字爆破
17.分析计算机检材,接上题,机主实际篡改多少微信数据?[标准格式:1]
参考答案:3
解题思路:
通过取证软件解析结果和缓存库进行对比发现
对比第一处
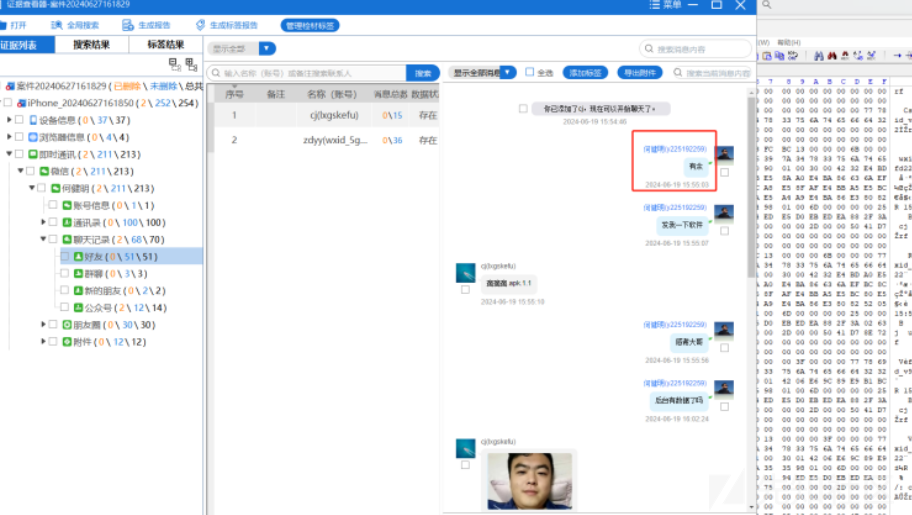
对比第二处
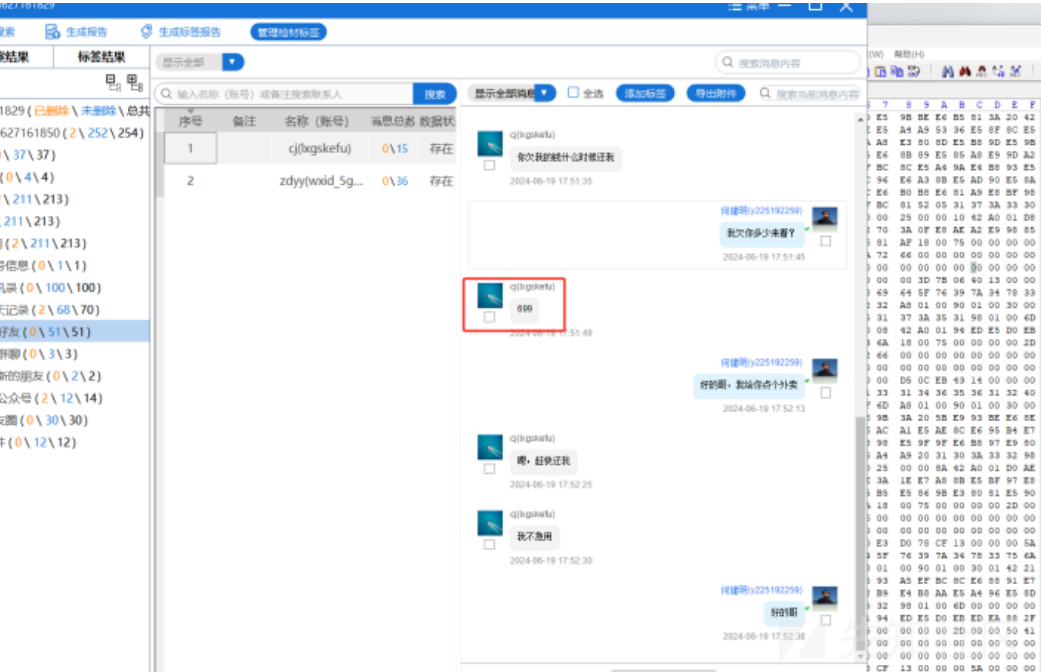
对比第三处
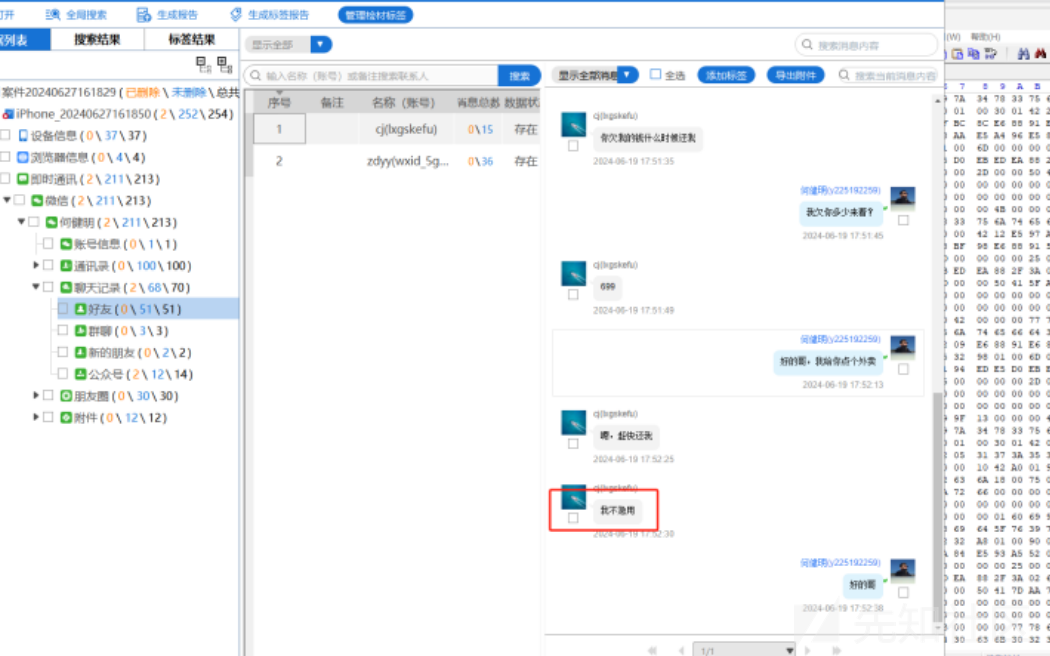
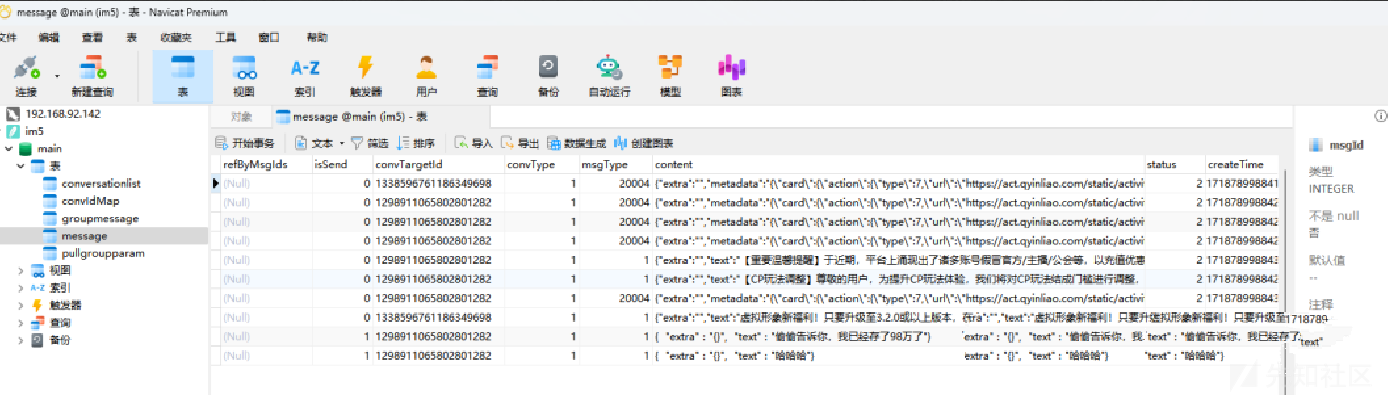
###18.分析计算机检材,接上题,机主共存款了多少金额?[标准格式:10万]
参考答案:98万
解题思路:

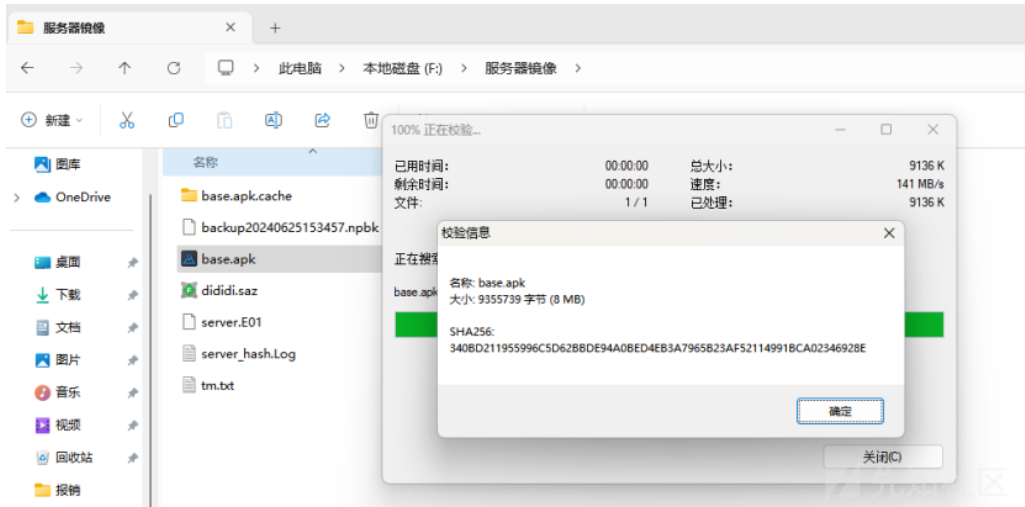
19.分析计算机检材,在手机模拟器中勒索apk软件的sha256值是什么?[标准格式:全小写]
参考答案:340bd211955996c5d62bbde94a0bed4eb3a7965b23af52114991bca02346928e
解题思路:
分析C:\Users\Administrator\backup.npbk模拟器备份文件
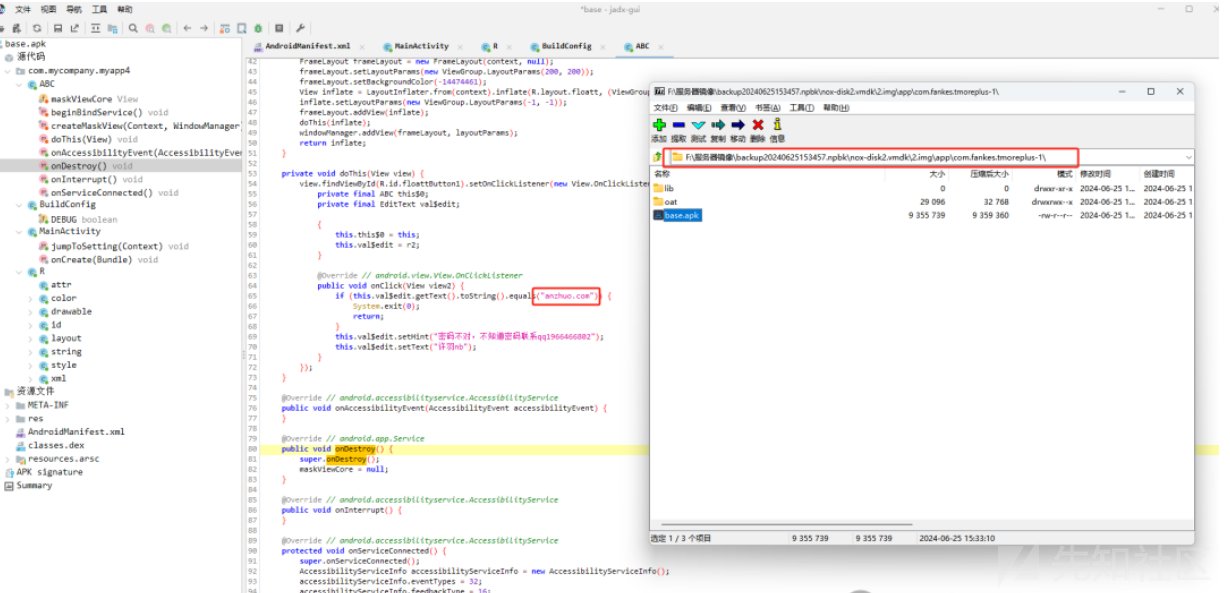
20.分析计算机检材,接上题,请问勒索apk软件的解锁密码是什么?[标准格式:qwer.com]
参考答案:anzhuo.com
解题思路:导出模拟器中目标apk,静态分析即可

DAMO开发者矩阵,由阿里巴巴达摩院和中国互联网协会联合发起,致力于探讨最前沿的技术趋势与应用成果,搭建高质量的交流与分享平台,推动技术创新与产业应用链接,围绕“人工智能与新型计算”构建开放共享的开发者生态。
更多推荐
 3
 0
- 0


 已为社区贡献3条内容

所有评论(0)